

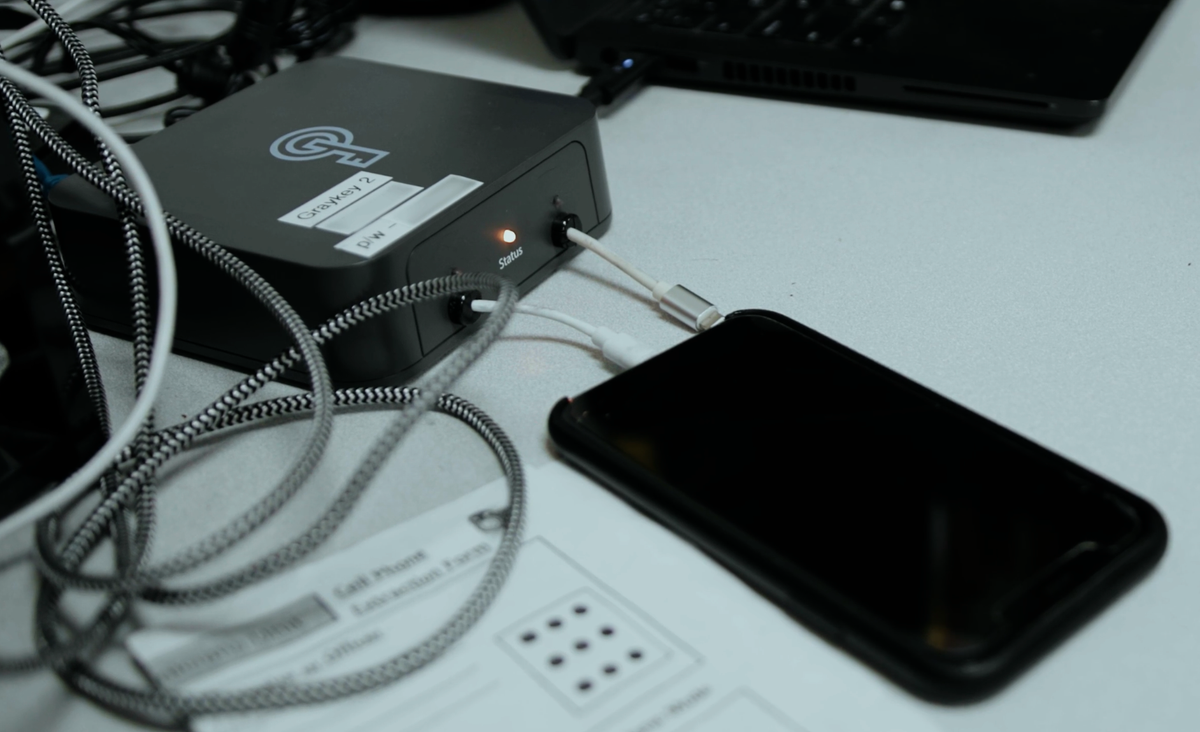
A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media.
This is the latest salvo in the never-ending battle between Apple and companies that help cops — sometimes those in authoritarian countries — break into iPhones.
In November 2024, 404 Media revealed Apple quietly introduced a new feature in iOS that automatically reboots an iPhone that has not been unlocked for 72 hours. The idea behind this so-called “inactivity reboot” is to revert the phone to a state that makes it harder for police to break into the device, and thus extract sensitive data from it with forensics technology.
At the time of Apple’s change, law enforcement agents expressed concern about this new feature, given that oftentimes they can’t immediately try to break into iPhones that have been seized. That could be because police are still waiting for a court authorization to do so, or there is simply a backlog of devices to unlock, for example.
So, y’all gonna switch to GrapheneOS now?
The companies who sell these bypass devices spend time on graphene too, don’t worry.
The price of iOS exploits would suggest Apple’s doing a pretty good job in this area.
I’m sure they do spend time on Graphene OS, but that’s not the same as being successful in cracking it.
Most of these exploits involve side channel attacks which are much closer to the hardware. Graphene definitely does a lot more to make that difficult, but typically devices are getting pwned within a few months even with graphene.
Having graphene on relatively new hardware is a really good practice, but it obviously isn’t a complete security posture on its own. Not having sensitive, compromising or incriminating stuff on your daily carry phone is much more important.
I remember one cybersec company got hit with an internal communications leak that suggested they could get into any GrapheneOS device before the Pixel 9, AFU or BFU. They were still having trouble with BFU Pixel 9. But this was a year or two ago.
Device wipe before capture/seizure seems to be the highest guarantee.
As someone with a Pixel 8 running Graphene OS, I’d love for you to cite the source so I could read it.
https://www.androidauthority.com/cellebrite-leak-google-pixel-grapheneos-security-3611794/
Appears I was partially misremembering, they were able to get into older phones on older security patches.
I wonder if they spend time on Linux mobile devices, considering how niche they are.
But then again, security through obscurity is not real security, and I’m not aware of any reasonable way to run something like QubesOS on a phone in any way that would be usable.
I’m sure they spend time on Linux in general, since it is the most common operating system (and includes Android, so even bigger). I doubt they spend much, if any, effort on the specific subset of systems that make a Linux phone different from another Linux device.
Smartphones had been vulnerable for pretty much it’s entire existence, and most of time, while true software do play a role, it’s been more about stuff such as bootloader exploits.
Sadly Linux phones on it’s state are insecure by design.
They don’t have to stay insecure by design. It just requires purpose-built hardware.
Does graphite disable faceid and touchid?
On Graphene, Lockdown mode disables biometric login until you unlock it manually with your passcode, but the device is still in the less secure AFU (After First Unlock) state.
You can also set it to restart the device if not used within a set time period. Various settings from 10 minutes to 72 hours. So if you haven’t touched your device within that time period, it will shutdown and restart, going back to the more secure BFU (Before First Unlock) state.
That’s no different than iOS in that regard then (minus the configurable restart time). But that’s about what I’d expect, not sure you could have a useable phone if it didn’t have an AFU state at all.
deleted by creator
It’s almost like there’s only two ways to actually accomplish this type of thing. You can do the same basic thing but use different names to differentiate where/how that function is used.
Lock it and require the passcode where the decryption key is still in memory because the system is running, or shutdown/restart the device so the decryption key isn’t in memory anymore.
What would a third option even look like?
Removed by mod
What are you babbling about? Of course, that’s why I already said it. Twice.
Both comments I have made in thi thread have mentioned shutting down or restarting the device to put it back into a BFU state.
Since you clearly didn’t actually read the comments you are replying to… I’ll include the relevant parts from both below:
You still didn’t answer the question I posed though… before replying in way that seems to indicate you either can’t, or refuse to actually read before responding condescendingly.
Since you seem to think there should be another choice instead of doing the same two things to protect the device/data… what would a third option look like? Other than locking and disabling biometrics, or a shutdown/restart putting the device back into BFU mode.
Or are you just stuck thinking a shutdown and reboot are technically different things? Even though that makes no difference here since they both put a device into BFU.
You can disable. You can also two factor it e.g. fingerprint and pin, with also a long password for BFU.
The fingerprint is the way in they are using. Bio entries are owned by the police if arrested. Finger/face/eye. Passwords/passcodes are not.
(Basically they own your body, not your mind without a warrant)
They are not supposed to own my body except as a punishment for crime whereof the party shall have been duly convicted.
/hj
Fingerprint and face is allowed under most states
Yeah, I was making a 13th Amendment ‘joke’, since you said “own”
Lockdown mode disables biometrics while still leaving your device on, say if you know you’re going to talk to the police and don’t want to be forced to provide biometrics to unlock the device. And you can setup an automatic reboot after a set time period where it would return to a BFU state automatically.
deleted by creator
Let me clarify: when I meant two factor, I mean both. You need both the print AND the pin to unlock. So its more convenient than a full passphrase (for first unlock) but still requires knowledge not just biometrics.
Genuine question here. I don’t really get the idea of using print and then a pin. If I want more security, then I use the pin alone, if I want more convenience, then I use a print. Can someone please give me an example in which using both actually makes sense? I honestly don’t see how using both would benefit security, it certainly does not benefit convenience.
I can see the use of 2 factor with a PIN and then a hardware key like a yubikey, or a pin and then a password, that does make sense to me, focused on security alone and doing away with convenience.
The benefit is if your PIN was compromised your phone would still be inaccessible, barring them having you physically. It’s another layer of defense. Similar to a yubikey, if someone had your phone but not the extra hardware. Although I think using a yubikey every time I wanted to use my phone would be prohibitively inconvenient.
Also, I don’t think PIN and password would be considered 2 Factor. That’s essentially just a longer password.
In GrapheneOS you can set it so it requires both a password and a fingerprint
Ahh, yes. The old “I use this thing and because I use this thing it must be better than your thing.”
An apple user using graphene?
You are a funny person.