

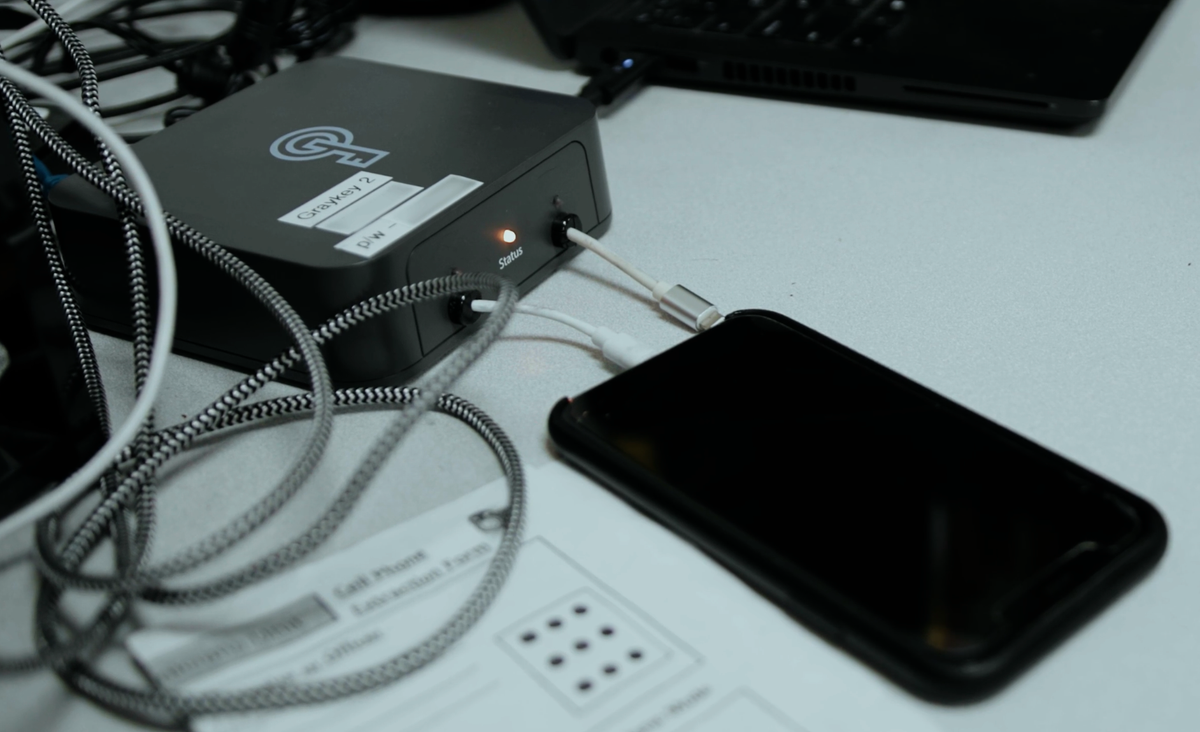
A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media.
This is the latest salvo in the never-ending battle between Apple and companies that help cops — sometimes those in authoritarian countries — break into iPhones.
In November 2024, 404 Media revealed Apple quietly introduced a new feature in iOS that automatically reboots an iPhone that has not been unlocked for 72 hours. The idea behind this so-called “inactivity reboot” is to revert the phone to a state that makes it harder for police to break into the device, and thus extract sensitive data from it with forensics technology.
At the time of Apple’s change, law enforcement agents expressed concern about this new feature, given that oftentimes they can’t immediately try to break into iPhones that have been seized. That could be because police are still waiting for a court authorization to do so, or there is simply a backlog of devices to unlock, for example.
I assume that would just be shutting down the phone. When it boots up it required the passcode, which is what they want to bypass here
No, this preserves the phone in an “after first unlock” state. They specifically dont want a phone to reboot or shutdown because then the encryption keys get dumped from memory and require the password to decrypt the keys.
Yeah… Aka if it was shutdown. It isn’t before first unlock state. So if you are going to get arrested, shutting the phone off mitigates all of this
Disclaimer: I only use iPhones for security testing, so this is more from related literature rather than first-hand experience.
IIRC the hardening unattended reboot could offer is already covered better by options like disabling biometric unlock, security key 2FA, enabling lockdown mode, enabling advanced data protection, disabling iCloud, disabling USB accessories, and so forth. Also unattended reboot seems like an easy prank vector or foot gun to render a device permanently inaccessible (i.e., device always reboots immediately after pin entry) requiring recovery mode reset or restore to fix.
A. If you want 2fa to unlock a phone fuck off B. One has to opt in to iCloud. (It’s way to fucking motivated and absolutely a forced thing in my opinion though)
If you can’t download an app without being signed into an account… You paved the way for Microsoft. Literally were the worst of the worst and made it so. Even the Microsoft store allowed $0 purchase without sign in for years after if not possibly still today. (I don’t use them).
That said… Security testing anything should tell you the Apple/Google/Microsoft system is all wayyyy more secure using 2FA and activation locks we all hate because theft is a thing. We shouldn’t need an original proof of purchase to unlock a device, yet we do because social engineering makes it that way.
Agreed, I’m pretty used to security key unlocks and still wouldn’t want that friction on a personal device.
Also just for completeness, since I forgot to mention: enabling stolen device protection and findmy/mdm to enable remote wipe.
Yeah, a security key for Apple disables you ability to receive the account with them.
Most smartphones encrypt the majority of their storage these days.
This means there are two states the phone can be in.
BFU, or Before First Unlock, is the most secure. When you power on the phone it has just enough software in unencrypted storage to come on, initialize its hardware, start some background processes, and display an unlock screen. This is the most secure state for the phone. When you type in your password, the password itself decrypts the actual key which is used to decrypt the main storage. Without that password, the data is essentially useless as it cannot be decrypted. Also, most phones are now set up so that if you try the wrong password 10 times, it will erase the main storage encryption key which means the data is completely unrecoverable forever. In general, it doesn’t matter what you can exploit BFU because there’s very little running to exploit and the storage encryption key is usually stored in a secure enclave, that is a special part of a chip that is designed to resist tampering.
Once you type in your password the first time, the phone is AFU, or After First Unlock. The key to access main storage is held in memory, it is being actively used to read and write from that storage as software is running on the phone like email, background apps, etc. The prompt to unlock the phone looks exactly the same, but in reality the phone is in a much less secure state. There’s plenty of software, both system and apps, running for you to try to exploit.
The point here is that if you set the phone to regularly reboot, or to reboot if you haven’t logged in in a day or two, each time it reboots it switches back to BFU state.
And so if some government agency has arrested you and seized your phone, you want that reboot to happen because if the phone automatically reboots before they manage to get into it, it becomes much much harder for them to get in.
Well said, that’s exactly what I was getting at. Apple has a Shortcut command that can switch to BFU - it’s called Reboot - but they specifically prevent users from setting it up to run on a schedule of their convenience. They might be afraid of accidental boot loops, or breaking wake up alarms, or something else - they haven’t published reasoning anywhere I’ve seen. But I think it’s pretty poor of them to restrict the feature.
deleted by creator